CMMC and NIST SP 800-171 readiness for defense contractors.
An assessor's eye, before the assessment. We prepare you for how an assessment actually goes: what gets asked, what counts as proof, and where companies that thought they were ready come up short.
NIST SP 800-171 is already in your contracts, and your customers are already asking. The companies that are ready will be the easy ones to pick.
LIVE · THE CLOCK HAS BEEN RUNNING
NIST SP 800-171 has been required in defense contracts for
3,192days
That's more than 8 years since the December 31, 2017 deadline in DFARS 252.204-7012.
CMMC didn't create the requirement. It started checking.
How we got here
JUN 2015NIST publishes SP 800-171: 110 requirements for protecting controlled information.DEC 31, 2017Deadline. Defense contractors must implement it under DFARS 252.204-7012.NOV 30, 2020Contractors must post a self-assessment score in SPRS (DFARS 7019 and 7020).DEC 16, 2024The CMMC program rule (32 CFR Part 170) takes effect.NOV 10, 2025CMMC requirements start appearing in contracts (48 CFR rule, Phase 1).TODAYPhase II paused. The 800-171 requirement is not.
The SPRS scale runs from −203 to 110Every contractor starts at 110 and loses points for each requirement not met.
−203
0
110 · every requirement met
A score is only as good as the evidence behind it. That's what the SPRS Score Check tests.
01 // WHAT WE DO
From "where do we start" to "we're ready."
Pick one piece or the whole path. Every engagement is led by someone who runs assessments for a living.
START HEREFIXED PRICE
SPRS Score Check
Defense contractors report their own security score to the government. We check whether your evidence actually supports the number. A score you can't back up is a liability, not just a number.
Quoted after a 30-minute call · 1 to 2 weeks
REPORTED VS. SUPPORTED
Reported
Supported
The gap is where the risk lives.
Scoping
Where controlled information actually lives and who touches it. A smaller, well-drawn boundary means fewer systems to protect and a cheaper assessment.
Readiness assessment
An assessor-style review against all 110 requirements, with the gaps ranked by what would actually fail you.
Security plan and policies
The documents that describe how you protect controlled information, written to match how your company really operates.
Mock assessment
A dress rehearsal run the way the real one will be, so your team hears the hard questions from us first.
FOR C3PAOS AND IT PROVIDERSA Lead CCA for subcontract assessments, and clear responsibility mapping for the providers who support defense contractors.
ScopeFind where controlled information lives. Draw the smallest honest boundary.
02
Find the gapsReadiness assessment against every requirement, ranked by risk.
03
Fix and documentYour team closes gaps; we direct and verify. The paperwork matches reality.
04
RehearseA mock assessment with the same questions and evidence requests.
Assessment dayYou walk in knowing what they'll ask, and what you'll show them.
03 // FOR ASSESSMENTS
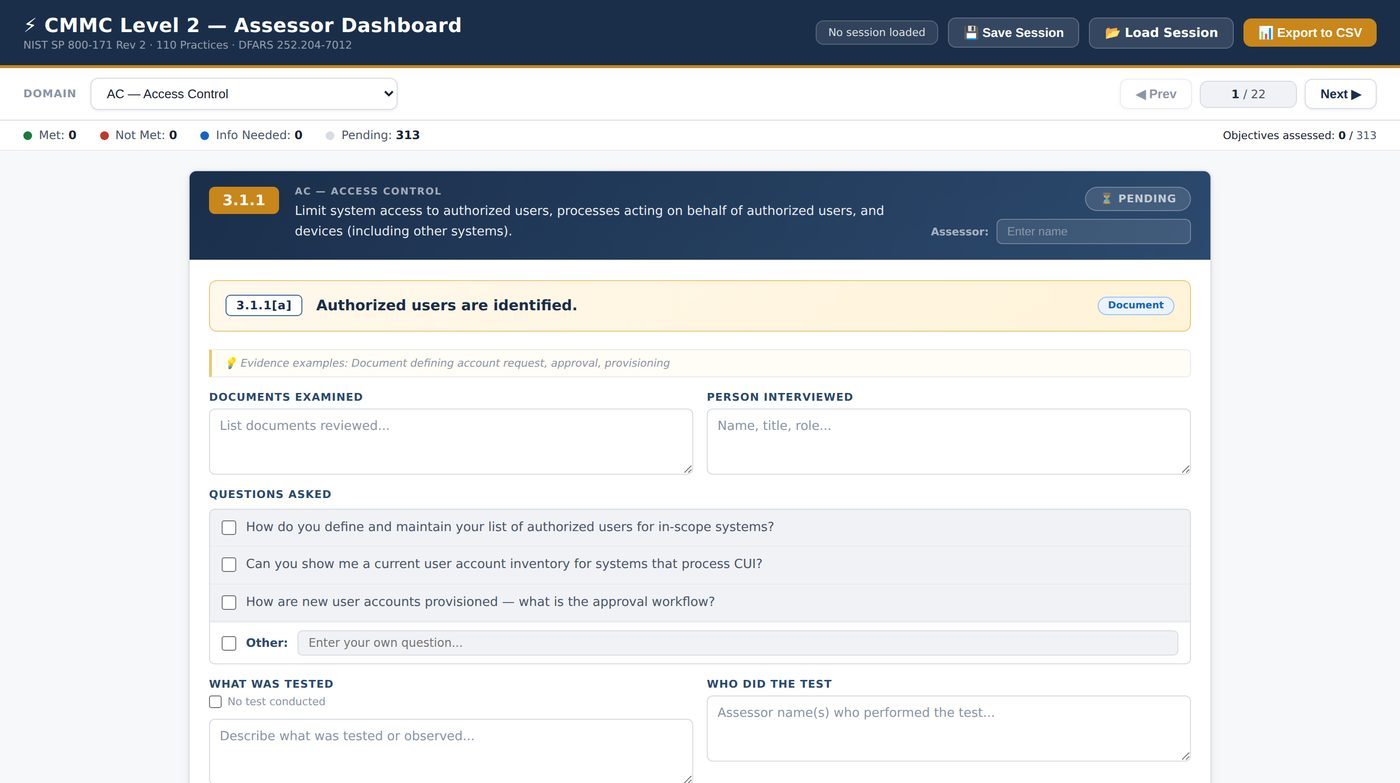
Lead assessor and assessor dashboards.
Available for assessments. They make reporting at the daily checkpoints and filling out the assessment templates much easier, so the team spends its time assessing instead of formatting.
✓Every objective with its evidence, interviews and tests in one place
✓End-of-day checkpoint reporting without the scramble
✓Results that drop straight into the assessment templates
04 // DO IT YOURSELF
Prefer to start on your own?
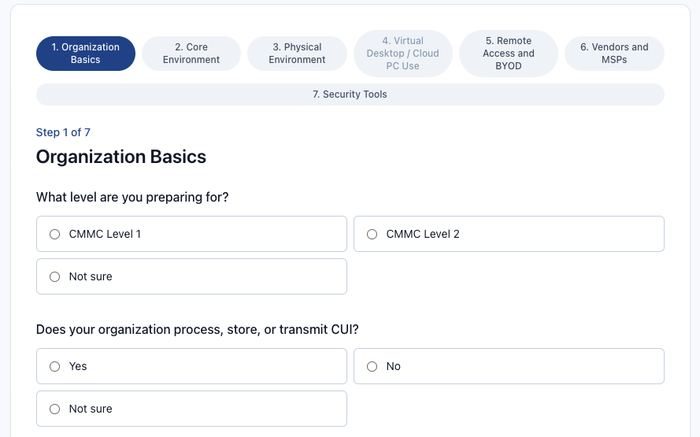
FREE · 7 SECTIONS · ABOUT 5 MINUTES
CMMC scope checker
What's actually in scope for your assessment, with an assessor-oriented estimate at the end.
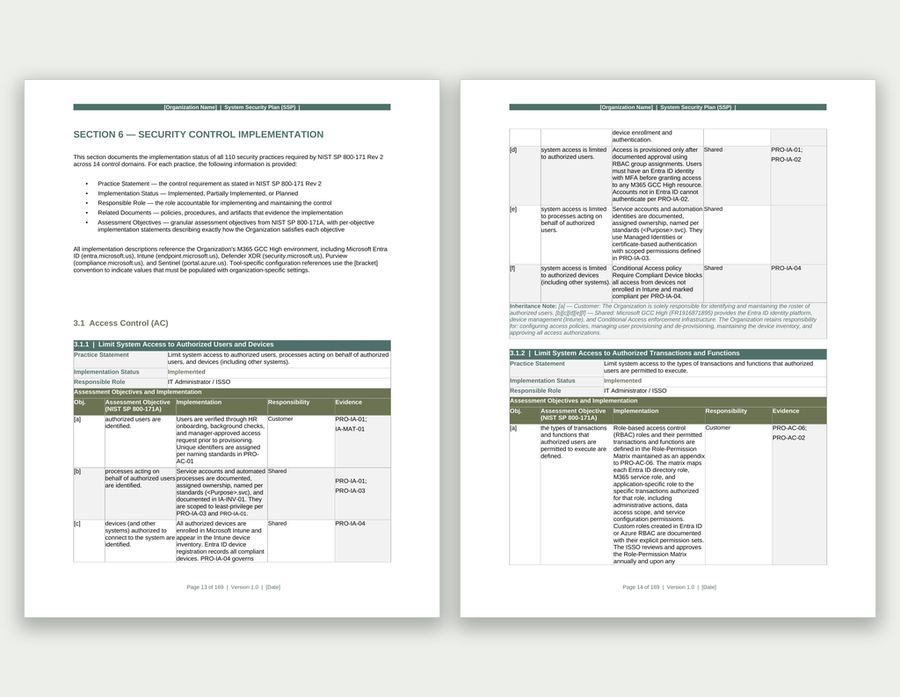
Every document your NIST SP 800-171 assessment needs, ready to fill in.
Policies, procedures, agreements, your System Security Plan, and every other document an assessor will ask for. Plus the roadmap, calendar and 600+ practice questions.
And the honest answers, including the ones that don't sell anything.
Should we wait until the certification timeline settles down?
NIST SP 800-171 is already required in most defense contracts, and primes are choosing suppliers now. Waiting is still a decision, and usually an expensive one.
What's the difference between a self-assessment and certification?
In a CMMC self-assessment, your organization evaluates its own environment against the applicable CMMC requirements, using evidence to support its findings. A consultant may help, but your organization remains responsible for the results, which are submitted to the Supplier Performance Risk System (SPRS). An authorized senior official must affirm continued compliance at the time of the assessment and every year after.
A CMMC Level 2 certification assessment is an independent evaluation by an authorized CMMC Third-Party Assessment Organization (C3PAO). Passing it establishes your Level 2 certification status. The results go into the CMMC reporting system and show up in SPRS for the DoD. Your authorized senior official must also affirm continued compliance after the assessment and every year after.
Can you prepare us and then assess us?
No. An assessor can't certify a company they helped prepare. We'll tell you up front which role we're playing.
How long does getting ready take?
Most organizations should plan 6 to 12 months to become genuinely ready for a CMMC Level 2 assessment. A well-controlled environment that already follows NIST SP 800-171 may be ready in about 3 to 6 months. Organizations with unclear CUI scope, major technical gaps or immature documentation often need 12 to 18 months or longer.
Do you do the technical fixes?
We direct and verify. Your IT team or provider does the hands-on work, which keeps our advice independent.