HOME / SUPPLY CHAIN RISK MANAGEMENT

Supplier security assessments for companies that depend on vendors.

Find out which suppliers you can actually rely on while you still have options. For defense primes, manufacturers, hospitals, and anyone else whose work runs through other companies.

Your organization PEOPLE · DATA · SYSTEMS Hospital Billing company Suppliers Cloud & software Remote vendors Defense customer SUPPLIER NETWORKCan they protect your data? VENDOR REMOTE ACCESSWho can reach you? SOFTWARE YOU DIDN'T WRITEHas it been tampered with? EVERYONE HAS A TIER 1 SUPPLIER Their security is part of your risk.
APPROVED ISN'T THE SAME AS USABLE

Supplier claims aren't supplier assurance. Most companies know what their suppliers say about security. Few have checked.

LIVE · YOUR SUPPLIERS' BAD DAYS

Their bad day becomes yours.

Sources: ransomware.live, HHS OCR breach portal, supplier dashboard sample
Manufacturing ransomware victims
33this week
Per week, last 12 weeks. Any one of them could be on your supplier list.
Breaches that came through a vendor 21% Share of this year's large healthcare breaches where HHS flagged an outside vendor.
What a buyer seesSample from the supplier dashboard, 20 suppliers
Certified by an assessor8
Self-assessed only5
Unconfirmed5
Expiring within 90 days4
UPDATED DAILY FROM PUBLIC SOURCES. SUPPLIER NUMBERS ARE SAMPLE DATA.
01 // HOW A SUPPLIER REVIEW WORKS

"Yes" is a start. A screenshot is better.

Questions and evidence, never scans. Built on the baseline the Department of Defense requires of every contractor.

01
AskEach supplier answers a short set of security questions.
02
VerifyWe ask for proof behind the answers that matter most.
03
RankEvery supplier sorted: solid, close, or a problem.
04
ReportWhere to focus, and what to ask each supplier to fix.
WE LOOK FORAre their computers managed and kept up to date?
WE LOOK FORDo logins require a second step, like a code on a phone?
WE LOOK FORIs anyone watching for trouble, in-house or through a service?
WE LOOK FORWho can get to your information, and how?
02 // WHAT WE DO

Know who you can rely on before the contract does.

START HERE

Supplier security assessment

Whether a supplier's security matches what they've told you, and whether it covers the work you're sending them.

Information flow mapping

What each supplier receives, what they create from it, where it lives, and who touches it.

Critical supplier risk ranking

Which critical suppliers could stall delivery, and how hard each would be to replace.

Approved supplier list upgrade

From "who we've used" to "who we can use for this job," before the award instead of after.

Contract and requirement review

Security obligations hide in statements of work and attachments. We find them before you price the work.

Readiness coaching for suppliers

For suppliers who want to be the easy choice: a clear plan to close gaps and explain their security with confidence.

03 // FREE SELF-CHECKNEW

Supplier quick check

Answer a few questions about one supplier and see where they'd land in a full review.

GoReady for the work
ConditionsGaps, with a plan
HoldToo many unknowns
No-goNot for this job
Start the check
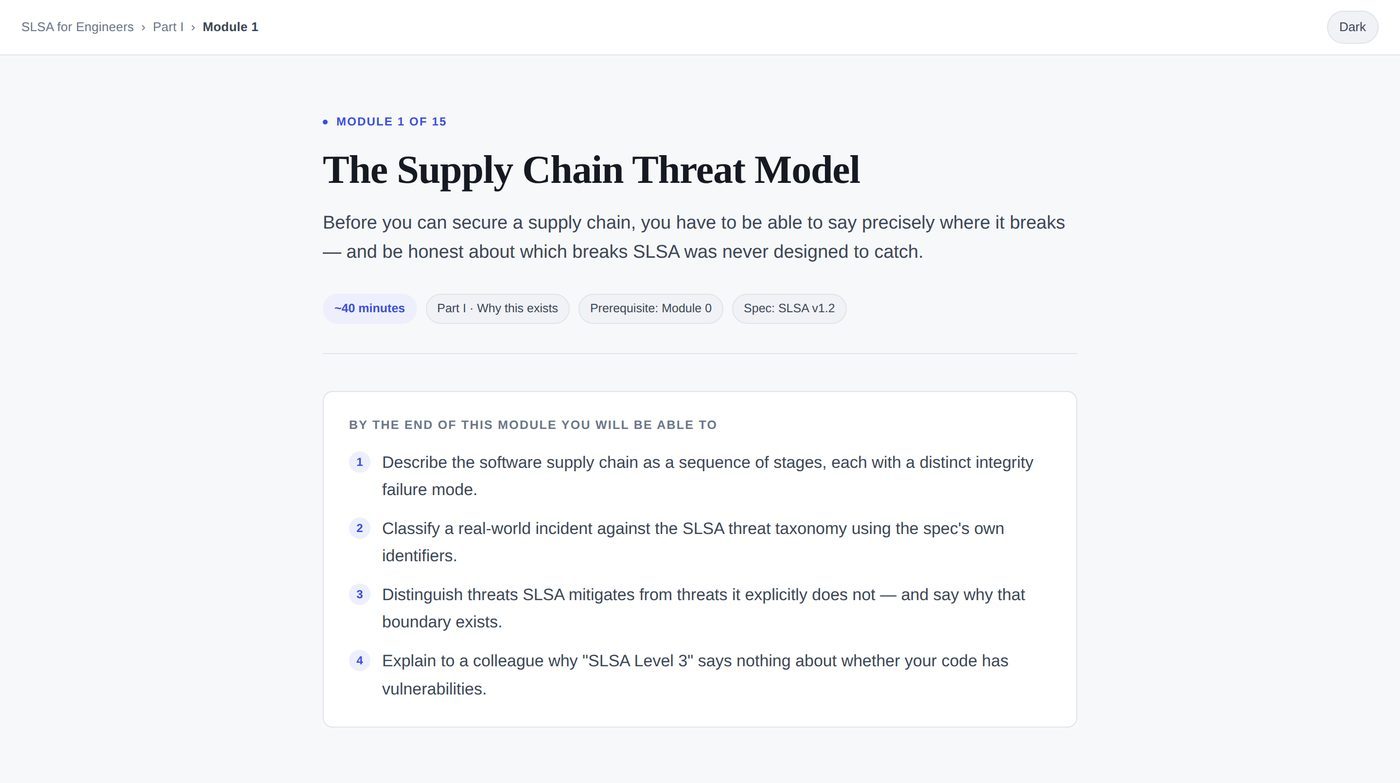
Opening page of the SLSA for Engineers course
SOFTWARE SUPPLY CHAIN

Your software is a supplier too.

The code you buy, build or download has its own supply chain. Our SLSA for Engineers course teaches teams how to prove it hasn't been tampered with.

See the course
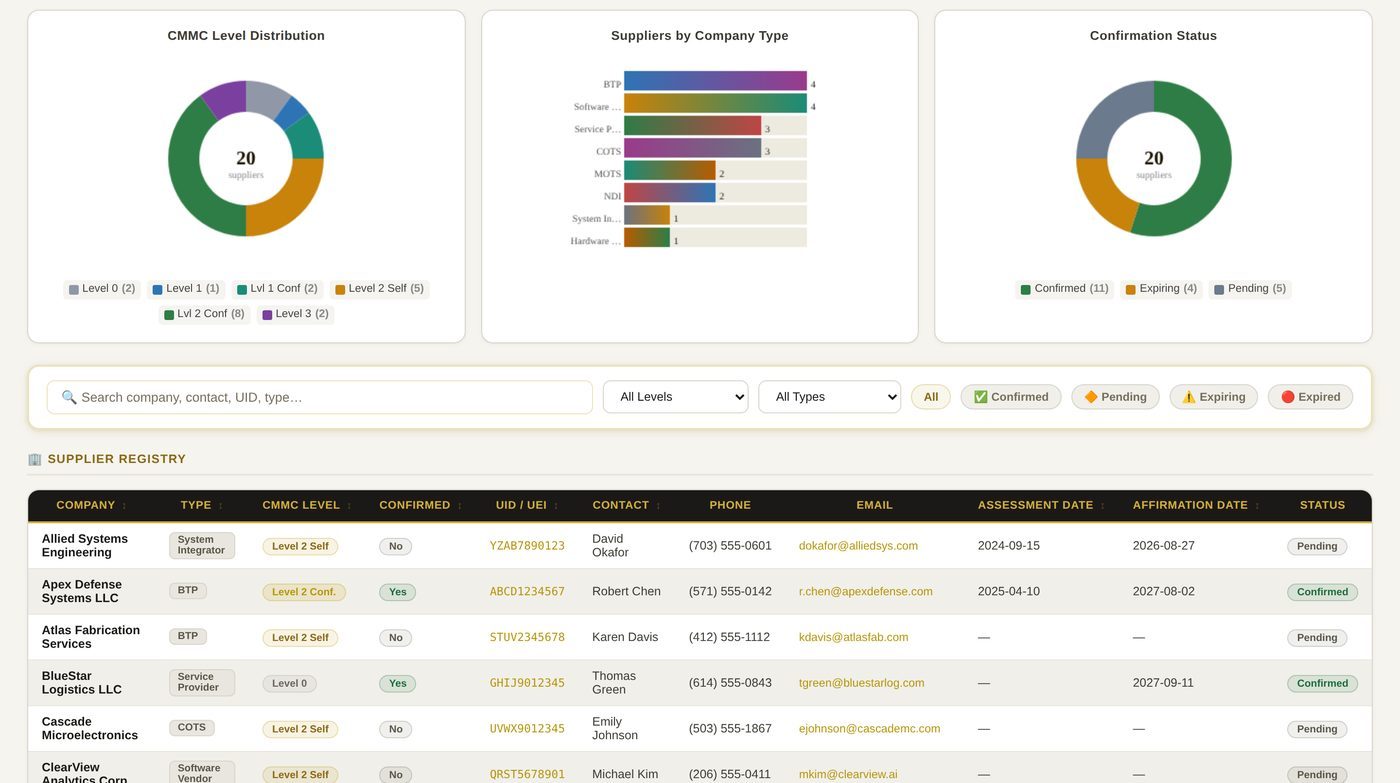
Supplier risk dashboard with charts of supplier status and a searchable supplier registry
04 // ONE VIEW OF EVERY SUPPLIER

The supplier risk dashboard.

Every supplier's status, open gaps and expiring commitments in one place. Load a spreadsheet and go. It runs inside your own network.

SELF-HOSTED · COMING SOON · DEMO DATA SHOWN
05 // QUESTIONS

The ones buyers ask.

Is this only for defense contractors?

No. Anyone who depends on vendors can use it: primes, manufacturers, hospitals checking their billing companies, and everyone in between.

Do you scan our suppliers' networks?

No. It's questions and evidence. We never touch a supplier's systems.

What if a supplier won't cooperate?

That's an answer too. An unknown supplier is a risk you're carrying, and the report says so.

How is it priced?

Pricing is tailored to your organization's needs. Fractional Security Leadership engagements are structured as fixed monthly retainers. Your monthly investment is based on how complex your environment is, the regulatory and contractual requirements you have to meet, your current security maturity, the improvements you have planned, and how much ongoing access and support you need.

After an initial discovery and risk review, you get a clear monthly proposal that spells out the service level, meeting schedule, advisory availability, deliverables, response times and anything that falls outside the retainer. See pricing.

FREE DOWNLOADS

Take these with you.

Checklists and samples are free to download. Fillable templates just need an email address.
All downloads →
FREE CHECKLISTSUPPLY CHAIN · 2 PAGES

Security Terms for Vendor Contracts

What to put in writing before a vendor touches your data or systems: incident notice, evidence, your right to check.

Download the PDF
FILLABLE TEMPLATESUPPLY CHAIN · 3 PAGES

Supplier Security Questionnaire

A short questionnaire to send one supplier, plus a one-page guide for reading the answers. Fillable.

SAMPLE DELIVERABLESUPPLY CHAIN · 3 PAGES

Sample Supplier Security Review

What our supplier review report looks like, for a fictional machine shop with six suppliers. Ratings, gaps, conditions and next steps.

Download the PDF
// READY WHEN YOU ARE

Is your security posture keeping you up at night?

Thirty minutes, no slide deck. Tell us what you're up against and we'll tell you honestly whether we can help.