Outsourced security leadership for anyone who handles patient data.
Hospitals, clinics, physical therapy practices, billing companies, and every other organization that holds electronic patient health information. We make you a harder target for ransomware, so you can worry a little less.
Passing an audit and surviving an attack aren't the same thing. We build to the federal government's own security standard, and HIPAA comes along for the ride.
LIVE · HEALTHCARE BREACHES THIS YEAR
The numbers every healthcare leader should see.
Sources: HHS OCR breach portal, ransomware.live
373large breaches reported this year
66.4Mpatient records affected
90%caused by hacking or IT incidents
19healthcare ransomware victims this week
Breaches by month, by cause
Hacking / IT incidentOther causes
Breaches involving an outside vendorShare of this year's large breaches where HHS flagged an outside vendor or billing partner. When one of them goes down, their hospitals go with them.
UPDATED DAILY FROM PUBLIC SOURCES
01 // ANATOMY OF A RANSOMWARE WEEK
It rarely starts with a hacker. It starts with a Monday.
MON · OVERNIGHTQuiet wanderingOne open network, so the attacker reaches servers, backups and partner links.
WED · 2:00 AMEverything locks at onceFiles and backups are encrypted together. The ransom note arrives.
WED · 8:00 AMEverything stopsPatients wait, revenue stops, and the phones start ringing.
WEEKS LATERThe long tailBreach notices, regulators, and every client asking what happened.
Every step is a place it could have been stopped. Our job is finding those places first.
02 // WHAT WE DO
A security lead, without the full-time salary.
An assessment to start, then a monthly retainer sized to your organization. We direct and verify; your team and vendors do the hands-on work.
START HERE
Security assessment
How your network is built, who has access, how vendors connect, how well your policies match reality, and how ready you are if something goes wrong. A plain-English report ranked by what matters most.
ONE EFFORT, BOTH BOXES
HIPAA risk assessment support
HIPAA requires every healthcare organization to complete a risk assessment. We use what we learned in the security assessment to help you complete yours, so the paperwork reflects how you actually operate.
Network design review
Where walls belong so one bad day doesn't spread.
Vendor access review
Who can reach your systems from outside, and whose job it is to secure each connection.
Security roadmap and runbooks
A prioritized plan with owners and dates, plus steps your IT team can follow.
Security policies
Written for how your organization actually runs.
Penalty-reduction evidence file
If the worst happens, federal regulators must consider the security practices you had in place over the prior 12 months. We keep that proof current, so it's ready on the worst day of your year.
Board and leadership reporting
Monthly progress, quarterly compliance summaries, and a briefing a CEO can read in five minutes.
03 // WHY VENDORS MATTER
When one vendor goes down, everyone connected goes with it.
Billing companies, IT providers and software vendors connect to many practices at once and hold data from all of them. That makes them some of the most valuable targets in healthcare. If you are one, this is about you. If you use one, it is about them.
A billing company is the classic example: one compromise, many victims. That's why we start with the connections.
04 // FREE SELF-CHECK
Ten questions. An honest answer.
Find out how exposed you are to ransomware in about five minutes, and get your top three fixes in plain English.
RANSOMWARE READINESS CHECK
Question 3 of 1030%
Could someone with a regular staff password delete your backups?
Yes, probablyNo, backups have separate accessI honestly don't know
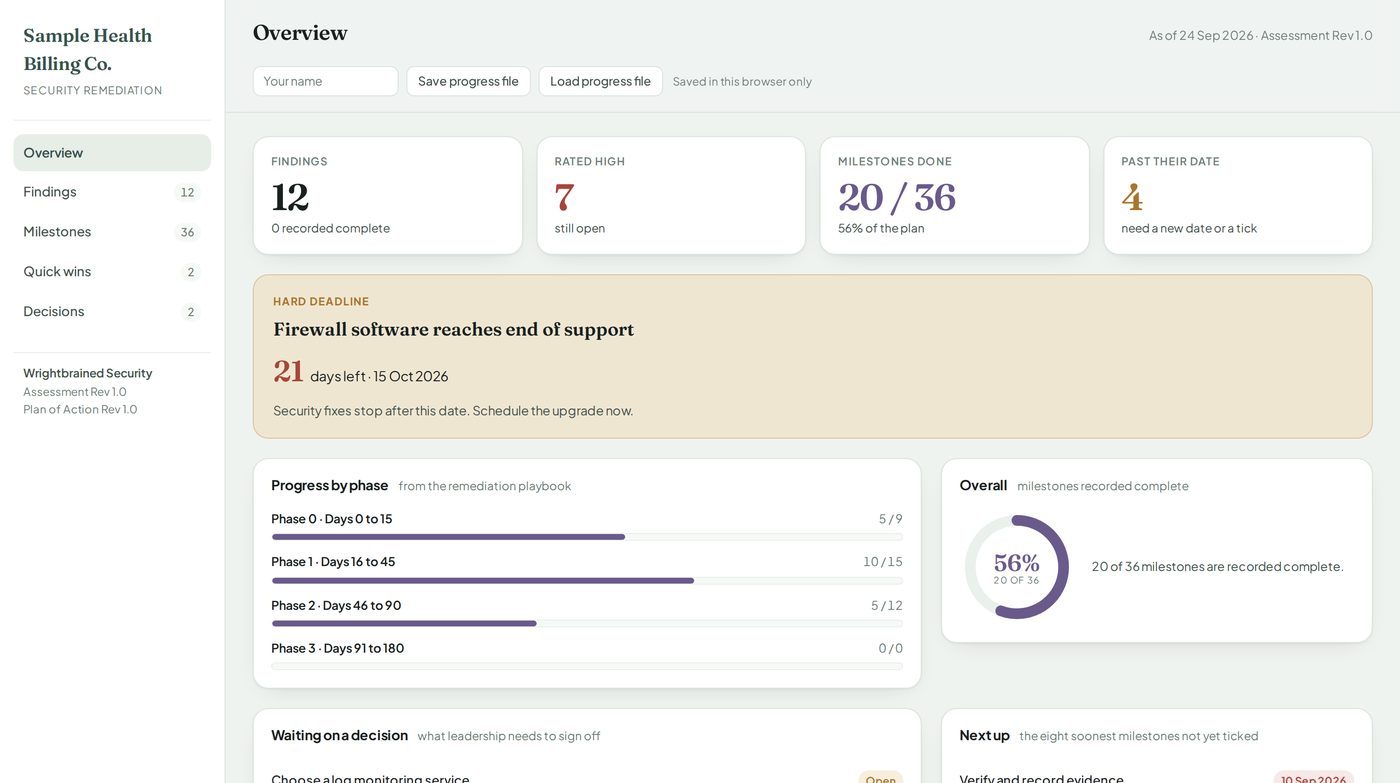
Findings, fixes, deadlines and decisions in one view. It runs inside your own network, so we never host or see your data.
SELF-HOSTED · COMING SOON
Sample data shown.
06 // QUESTIONS
The ones healthcare leaders ask.
Is this a HIPAA audit?
No. It's a security assessment built to a stricter federal standard. We help you complete the risk assessment HIPAA requires along the way.
Do you replace our IT provider?
No. We direct and verify; your IT team or provider does the hands-on work. We're the independent eyes making sure it gets done right.
Do you scan our network or try to break in?
No. We interview your team, review your design and evidence, and tell you where you're exposed.
What does the monthly retainer include?
The Fractional Security Leadership Retainer gives your team ongoing access to an experienced security leader who helps turn assessment findings into action and keeps you ready. Each month includes:
Remediation planning and oversight: a prioritized roadmap with clear owners, timelines and guidance on risk-based decisions.
Regular leadership meetings: review progress, clear blockers and get ahead of upcoming decisions.
Implementation guidance: scheduled time for your staff's questions about proposed technical or procedural changes and how they address security requirements.
Documentation and evidence review: policies, procedures, security plan updates, diagrams and supporting evidence, checked for gaps before anyone else looks.
Coordination and executive reporting: help aligning internal teams and service providers, with clear reporting on what is done, what is blocked and where leadership input is needed.
Ongoing readiness monitoring: tracking remediation progress, outdated evidence, bottlenecks and changes that could affect your readiness.
Your team carries out the changes and keeps responsibility for day-to-day operations and final business decisions. Hands-on engineering, incident response and work beyond the agreed scope are handled separately. You get the leadership needed to keep security improvements moving and make informed decisions, without hiring a full-time security executive.
FREE DOWNLOADS
Take these with you.
Checklists and samples are free to download. Fillable templates just need an email address.
 WRIGHTBRAINEDSECURITY
Book a call